Outsource IT Blog

IT, cybersecurity and cloud insight for Ontario businesses

303 articles and security alerts written by the Outsource IT team in Burlington, covering the threats, tools and decisions facing growing organizations.

Signed in to Google? Pin Outsource IT so our security alerts appear first when you search.

363 results

Security Briefing

October 13, 2026 · 3 min read

Anthropic Warns AI Models Could Soon Build Autonomous IoT Botnets

Frontier AI lab Anthropic has warned that small artificial intelligence models may soon develop the ability to self-replicate across connected IoT equipment. These models could form autonomous worm botnets across devices like smart appliances and off-brand streaming boxes. Because these networks operate without a centralized shut-off mechanism, businesses could find future infections exceptionally difficult to dismantle.

Security BriefingsMalware
Security Briefing

October 13, 2026 · 3 min read

Docker Resolves Critical Flaw Allowing Container Image Impersonation

Docker has fixed a critical vulnerability in Docker Hub that allowed users to push, pull, or delete container images under another user's identity. The issue existed for two years within the feature that converts personal accounts into organizations. Although Docker found no evidence that the vulnerability was exploited, unauthorized modifications to container images pose significant risks to application security.

Security BriefingsSupply chain
Security Briefing

October 13, 2026 · 3 min read

Hackers Exploit Three Zero-Day Flaws in Ivanti Connect Secure VPN

Attackers are actively chaining three zero-day vulnerabilities in Ivanti Connect Secure VPN appliances to take full root control without needing login credentials. Ivanti has released security fixes for two of the flaws, but a patch for the third remains pending. Canadian businesses using these VPN appliances face a serious risk of total network compromise and should act immediately.

Security BriefingsActively exploited vulnerability
Security Briefing

October 13, 2026 · 3 min read

Critical SAP Cloud SDK Flaw Risks Exposure of Login Credentials

SAP has warned of a maximum-severity vulnerability in its Cloud SDK for Python that could expose sensitive authentication secrets. If exploited, an attacker who controls a tenant subdomain can intercept OAuth2 client credentials used by cloud applications. This allows unauthorized actors to impersonate legitimate services and compromise business systems.

Security BriefingsCloud and identity
Security Briefing

October 13, 2026 · 3 min read

GitHub Fixes Flaw That Left 1,500+ Software Packages Open to Hijacking

GitHub has resolved a flaw in the npm package registry that allowed attackers to publish unauthorized updates to other users' packages without stealing credentials. The vulnerability left more than 1,500 software packages open to potential takeover before safeguards were introduced. Flaws of this nature can allow malicious code to enter trusted software supply chains that organizations rely on.

Security BriefingsSupply chain
Security Briefing

October 13, 2026 · 3 min read

Ad Tech Firm Xandr Fined Record €8.6M Over Sensitive Data Sharing

Microsoft advertising subsidiary Xandr was fined 8.6 million euros by Norway's data protection authority for illegally transmitting sensitive Grindr user data to advertisers. Regulators issued the record penalty because the platform shared personal details revealing sexual orientation without a valid legal basis. This highlights the severe financial and regulatory risks businesses face when third-party ad networks mishandle customer information.

Security BriefingsData breach
Security Briefing

October 13, 2026 · 3 min read

AI Accelerates How Attackers Escalate Access Using Stolen Accounts

Attackers are increasingly using artificial intelligence to rapidly scan networks and escalate privileges after stealing legitimate credentials. Because AI speeds up reconnaissance and exploitation, attackers can compromise sensitive systems faster than standard teams can investigate. A seemingly normal login can quickly turn into a major breach if post-login behaviour is not actively monitored.

Security BriefingsCloud and identity
Flaws in LG Smart TVs Allow Full Device Takeover on Local NetworksSecurity Briefing

October 13, 2026 · 3 min read

Flaws in LG Smart TVs Allow Full Device Takeover on Local Networks

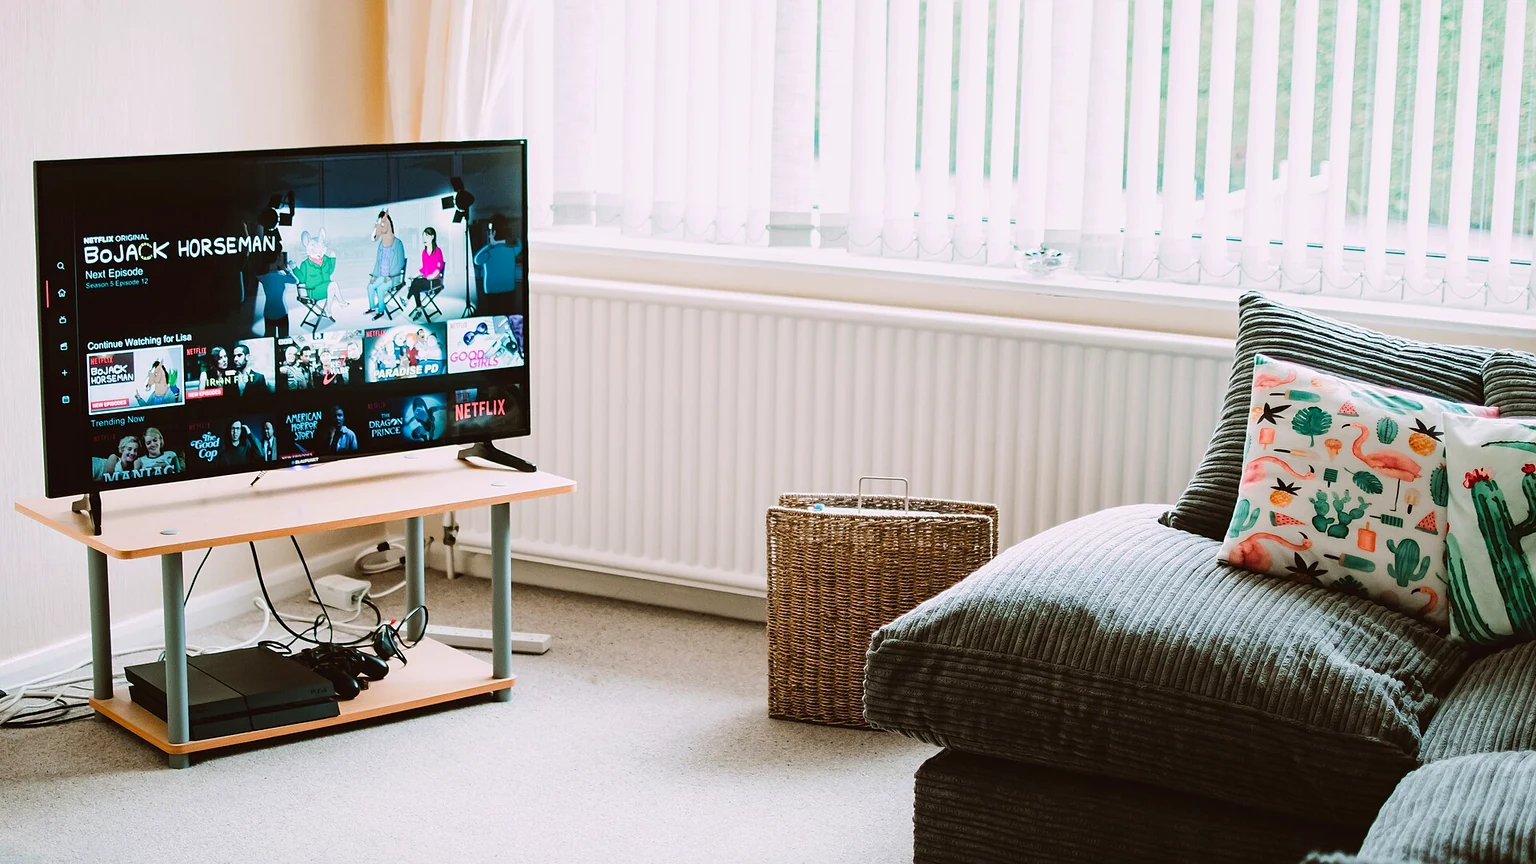
Security researchers identified three chained flaws in LG smart TVs that allow an attacker on the same local network to gain complete administrative root access without needing a password. If vulnerable displays are connected to your office network, an attacker could seize full control of the device without any user interaction. LG has released a security patch to resolve the vulnerability chain.

Security BriefingsActively exploited vulnerability
Hidden AI Tools and Browser Extensions Put Company Data at RiskSecurity Briefing

October 13, 2026 · 3 min read

Hidden AI Tools and Browser Extensions Put Company Data at Risk

Employees are increasingly adopting web chat assistants, browser extensions, and local AI runtimes that leave no footprint in standard software lists. Because these applications operate quietly in browsers or development tools, staff can easily paste or process proprietary business information without oversight. Without direct visibility into these tools, organizations face substantial risks of unintended corporate data leakage.

Security BriefingsData breach
Attackers Remotely Hijack Commercial Fridge ControllersSecurity Briefing

October 13, 2026 · 3 min read

Attackers Remotely Hijack Commercial Fridge Controllers

Cyber attackers remotely hijacked Danfoss refrigeration controllers across hundreds of French grocery stores, heating units up to 50°C and forcing operators to spoil inventory. The breach highlights the severe physical and financial disruption that can occur when internet-connected building systems are compromised. Any organization relying on third-party maintenance firms to remotely manage equipment is exposed if those remote connections lack strong safeguards.

Security BriefingsSupply chain
Critical Flaws in MarkLogic Database Allow Low-Level Users to Gain Admin ControlSecurity Briefing

October 13, 2026 · 3 min read

Critical Flaws in MarkLogic Database Allow Low-Level Users to Gain Admin Control

Progress Software has disclosed 31 security vulnerabilities in its MarkLogic Server database, rating five of them as critical. Two of the most severe flaws allow users with only limited management permissions to take persistent administrator control of the entire server. Businesses using this database software face severe risks to data integrity and system control if systems remain unpatched.

Security BriefingsCloud and identity
GitLab Fixes Maximum-Severity Flaw Allowing Remote Code ExecutionSecurity Briefing

October 13, 2026 · 3 min read

GitLab Fixes Maximum-Severity Flaw Allowing Remote Code Execution

GitLab has released updates to address a maximum-severity security flaw impacting both Community Edition and Enterprise Edition installations. Under certain conditions, unauthenticated attackers can execute arbitrary code on the server through a specially crafted regular expression in a CI/CD pipeline. Without prompt patching, unauthorized parties could compromise your development infrastructure and server environment.

Security BriefingsSupply chain
Budget Android Phones Found Shipping with Preinstalled Firmware MalwareSecurity Briefing

October 13, 2026 · 3 min read

Budget Android Phones Found Shipping with Preinstalled Firmware Malware

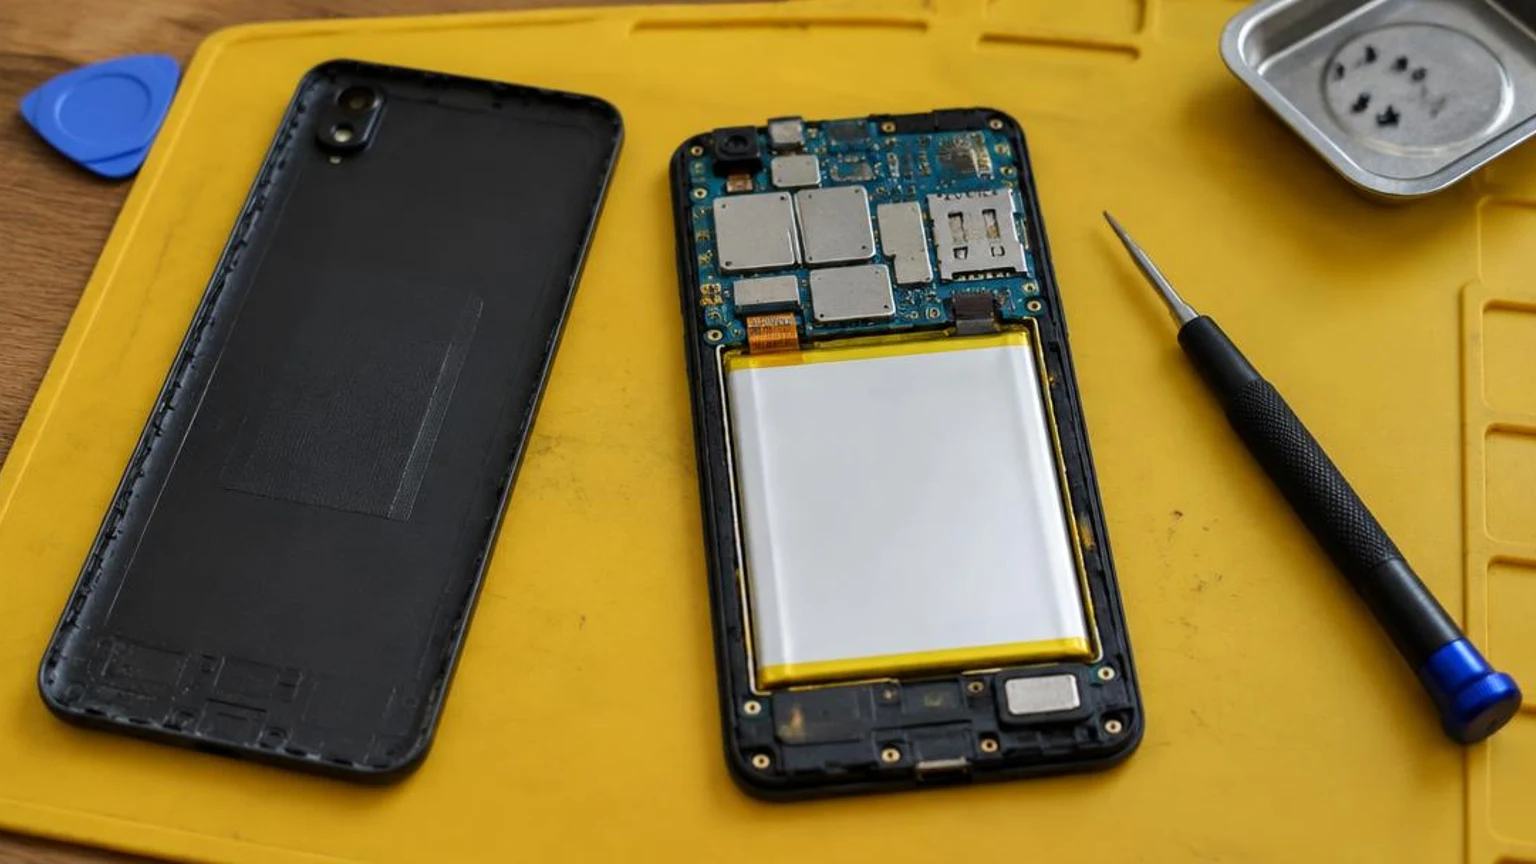
Low-cost Android smartphones have been discovered shipping with malware preinstalled directly into their firmware. Tracked as Midnight Mimosa, the threat covertly installs unwanted apps, conducts ad fraud, and turns infected phones into residential proxies. Unvetted devices connected to business resources can expose your organisation to illicit traffic and compromised security.

Security BriefingsSupply chain

Testimonials

Don't just take our word for it.

  • We were introduced to Outsource IT at a time when we were interested in improving our IT infrastructure and associated services. In working with Outsource IT; they have rebuilt our confidence in third party IT administration. As CBM grows, we know we are in good hands as we focus on serving our clients.
    Canadian Business MachinesFull service designer and precision metal fabricator.
  • Over the past 8 years, we have received exceptional service from Outsource IT. Their attention to our needs has been prompt and thorough and we are pleased to have them as our ongoing IT service provider.
    Hamilton Family Health TeamOntario's largest Family Health Team with over 150 doctors
  • Outsource IT has brought critical thinking, support and value to our Organization. Their attention to detail and strategic approach leverages I.T. operations to meet today's industry standards. Being EXCEPTIONAL is exactly what Outsource IT has brought to CICC.
    CICCCollege of Immigration and Citizenship Consultants

Technology partners we build on

Certified expertise across the platforms that run Canadian business, from Microsoft and Cisco to Fortinet, Dell and HPE.

  • Microsoft technology partner logo
  • Cisco technology partner logo
  • Fortinet technology partner logo
  • Barracuda technology partner logo
  • Dell Technologies technology partner logo
  • HP technology partner logo
  • Hewlett Packard Enterprise technology partner logo
  • Lenovo technology partner logo
  • VMware technology partner logo
  • Google technology partner logo
  • Eaton technology partner logo
  • 3CX technology partner logo